
When someone visits your application's hostname, something must accept the connection and send it to the right Kubernetes Service. An Ingress controller or gateway performs that job, often handling HTTPS certificates and routing by hostname or URL path as well.
Ingress and Gateway API describe routing rules in Kubernetes; a controller implements those rules. Gateway API gives shared infrastructure and application routes separate resources. Installing its definitions alone does not install a working proxy. You still need an implementation such as Envoy Gateway, Cilium's Gateway support, Traefik or a provider-managed gateway.
Envoy Gateway manages an Envoy proxy for gateway traffic. Cilium adds gateway capabilities to its broader Kubernetes networking system. Traefik is a reverse proxy with Kubernetes routing integrations. Compare Envoy Gateway versus Traefik when selecting a dedicated gateway, and assess Cilium when it already supplies your cluster network. A managed gateway can suit a team that prefers the cloud provider to handle more of the infrastructure.
The community ingress-nginx controller retired in March 2026. That does not retire the Ingress API or F5 NGINX Ingress Controller, which is a separate project. Identify the controller you actually run before deciding to migrate.
Choose a gateway for the traffic your application uses
If your platform team already operates Cilium, assess its Gateway integration within that supported platform. If you want an independently operated Envoy-based gateway, evaluate Envoy Gateway. Traefik is another candidate for teams needing a path across Ingress and Gateway resources. Cloud-managed gateways can reduce controller operations but introduce provider-specific features and service limits. None is a universal winner.
- List protocols and traffic patterns: HTTP, gRPC, WebSocket, TCP, large uploads, streaming responses and long-lived connections.
- Inventory behavior beyond routing: authentication, source-IP handling, redirects, rewrites, rate limits, certificate ownership and access logs.
- Check the implementation's conformance report for the exact release. Passing core conformance does not establish support for every extension you use.
- Choose who owns gateway infrastructure and who may attach routes. Test cross-namespace permissions and certificate access explicitly.
Compare behavior, not checkbox totals
A routing rule that looks equivalent can change path matching, forwarded headers or backend TLS. A successful health check proves little about authentication and request transformations. Use recorded synthetic requests against both controllers, then compare status, headers, routing and latency under your workload. Keep sensitive production payloads out of the fixture.
Adoption and exit cost
Record cloud load-balancer costs, policy resources, custom annotations, extension APIs and troubleshooting ownership. A portable API reduces some coupling; it does not erase implementation differences. Keep the old data plane available during a staged cutover and agree on error-rate and authentication-failure thresholds before moving traffic.
This comparison is a decision framework based on upstream documentation, not a benchmark. The historical comparison remains useful for understanding old links; its product generations and feature claims should be read in their original period. Continue with the migration planning guide.
Build a request-level comparison
Use a small test application that can report the received method, path and selected headers. Give each test a hostname, request, expected backend, expected response and security expectation. This makes a controller decision reviewable without pretending that one product's annotation has a direct equivalent in every other implementation.
- Routing: check exact paths, prefixes, trailing slashes, overlapping hostnames, unknown hosts and an unavailable backend. Record which rule wins when several might match.
- Identity: test authenticated, expired, missing and malformed credentials. Check whether an unauthorized request reaches the backend and whether an authentication outage fails as intended.
- Transport: include long requests, WebSockets or gRPC where used, client disconnects, TLS termination and backend TLS. Match timeouts across the client, gateway and application.
- Request transformation: verify rewrites, redirects, preserved query strings, forwarded scheme and client address. Confirm the application trusts only the intended proxy path.
- Operations: test certificate replacement, gateway restart, rolling update and endpoint withdrawal. Confirm that a responder can identify a rejected route from status and logs.
Understand what the API standardizes
Gateway API separates infrastructure and application routing responsibilities. That separation is useful when a platform team controls shared gateways while application teams own routes. It still requires an agreed permission model. Decide which namespaces may attach to a listener and which cross-namespace references are allowed. An overly broad attachment policy can let an application claim traffic it should not receive.
Read the selected implementation's conformance and feature documentation for the release you intend to install. Distinguish a standard feature, an optional extended feature and a vendor-specific policy. Put every extension in the platform inventory so the next migration starts with a clear list of dependencies. An upstream example on a development branch is not a compatibility guarantee for an older installed release.
Make the shortlist small enough to test
For an existing Cilium installation with a supported configuration, evaluate whether its gateway capability meets the request matrix before adding another networking control plane. For a team that wants a dedicated gateway lifecycle, assess Envoy Gateway or another maintained implementation independently. For a cloud-managed option, check the provider's supported route features, provisioning delay, quotas and observability access alongside the recurring price.
Traefik's suitability depends on the particular APIs and middleware a workload needs. F5 NGINX Ingress Controller is a separate project with its own documentation and support model. Neither name similarity nor use of the NGINX proxy proves equivalence to community ingress-nginx. Use the controller image, repository and IngressClass from the actual installation to identify what is running.
Decide from evidence
Keep a short decision record: required behaviors, results for each candidate, unsupported cases, operating owner and rollback path. Prefer a target that passes the required cases with understandable operations. Do not reward optional features that the platform has no plan to run or support. Recheck the record when a major controller upgrade changes the behavior you rely on.
A shortlist by operating model
Choose columns
| Candidate | Best reason to evaluate | Verify before choosing |
|---|---|---|
| Envoy Gateway | Independent Gateway API control plane with Envoy | Extension policies, Gateway CRD ownership and required route features |
| Traefik | Ingress and Gateway adoption within one controller family | Existing annotations, middleware behavior and supported release |
| Cilium Gateway | Networking team already operates a supported Cilium platform | CNI/kernel constraints, feature support and upgrade blast radius |
| Managed cloud gateway | Provider-operated load balancing and integrations | Region, protocol limits, ownership and recurring charges |
4 rows
Historical Kubedex content
Original publication: 2018-09-11T17:14:12+00:00. Preserved for context. Commands, versions, prices and results below reflect the original research.
Last Updated on August 2, 2021
As far as I know this is the complete list of Ingresses available for Kubernetes. Technically ambassador isn’t an ingress but it acts like one which is good enough. As you can probably see I’ve made quite a large table comparing features.
For those who struggle with reading the image there’s a link to open the google sheet directly below. Feel free to leave comments and I’ll update this blog post with corrections.
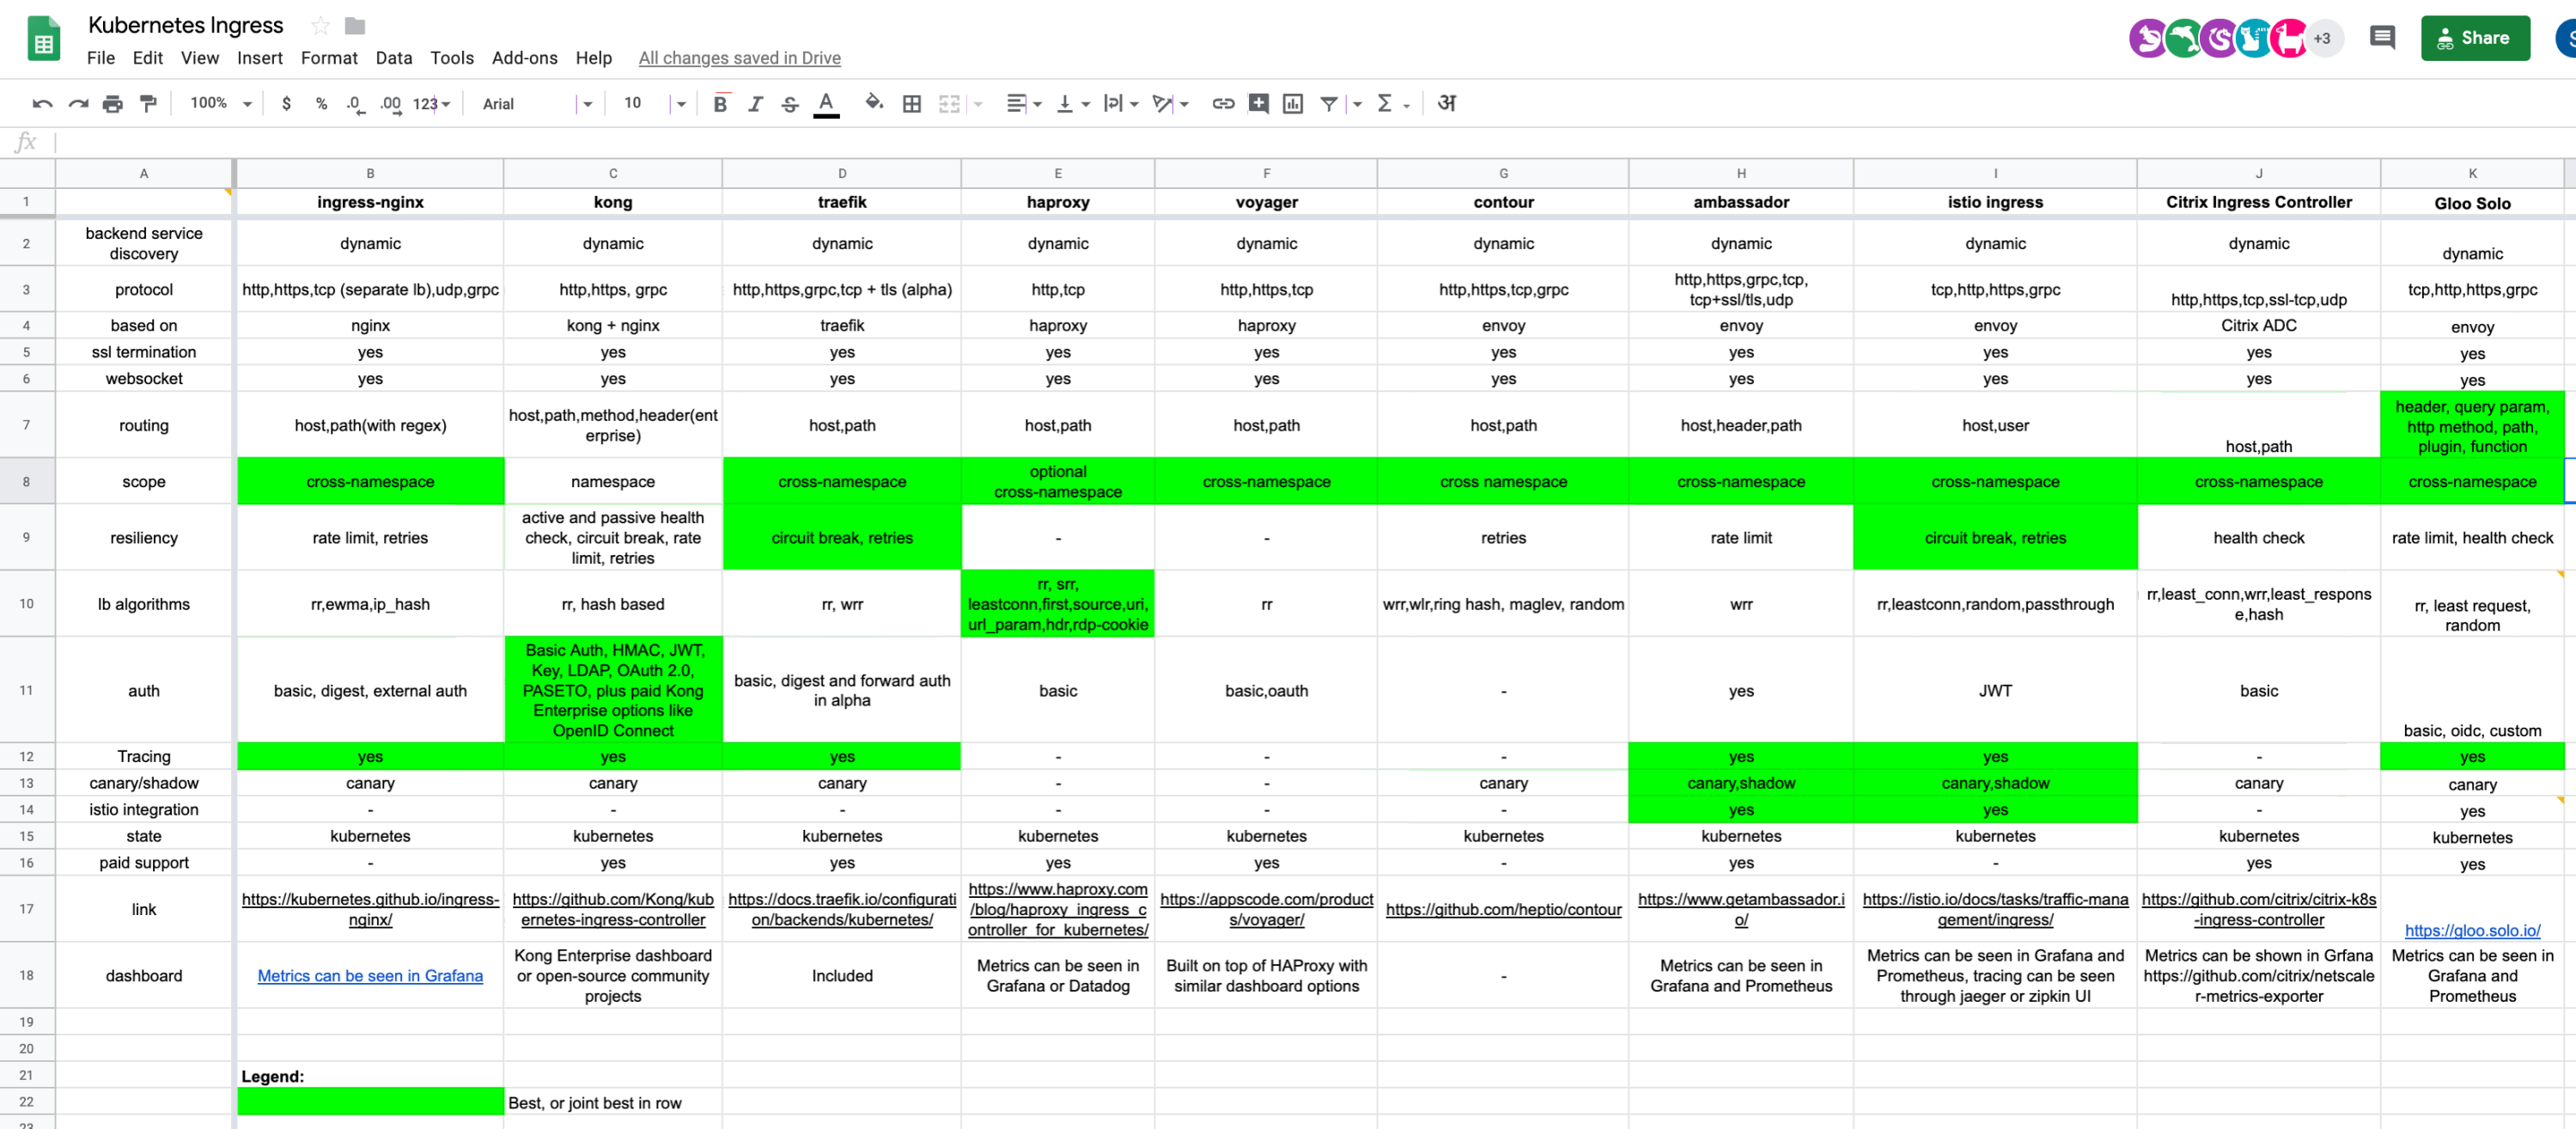
View the full Google sheet here.
Based on the features, my own experience and anecdotal blog evidence I’ll attempt to provide my usual unbiased opinion on each.
1. ingress-nginx
This is probably the most commonly installed ingress. Safe, boring and reliable. Supports http, https and does ssl termination. You can also get TCP and UDP working but from looking at the Github issues I think I’d try to avoid it. You get quite a few nice load balancing options as well as powerful routing, websocket support, basic authentication and tracing.
It’s quite common to use this ingress in conjunction with cert-manager for generating SSL certs and external-dns for updating cloud based DNS entries.
The lack of dynamic discovery is a bit of a downer. There is a config generator that you can use to automate this but apparently it’s terrible.
Note: There’s the official Kubernetes ingress which is what we’re talking about here. There’s also the Ingress from Nginx corp which has different settings.
2. Kong
Most people will use Kong when they want an API gateway. Kong includes a plugin system that extends the features to beyond what a normal Ingress would do. I wouldn’t use this as a generic http load balancer but if you want API management features then Kong is definitely a good choice.
At previous companies I’ve always put an ingress in front of Kong and routed /api/ requests to it. However, more recently the developers of Kong have been making a lot of progress turning Kong into an Ingress.
3. Traefik
This one surprised me with just how many features it has. The resiliency features look awesome and from reading a broad selection of tech blogs it seems quite stable. Supporting dynamic configurations is a big upgrade if you’re currently using ingress-nginx.
One downside is it only supports http, https and grpc. If you need TCP load balancing then you’ll need to choose something else. TCP is now in the Alpha release.
Another consideration is minimizing server reloads because that impacts load balancing quality and existing connections etc. Traefik doesn’t support hitless reloads so you need NGINX or Envoy Proxy for this. For a lot of people this is a big deal.
4. HAProxy
This is the king of the ingresses when it comes to load balancing algorithms. It’s also the best choice for load balancing TCP connections. HAProxy has a track record of being extremely stable software. You can also get a paid support subscription if you want one.
5. Voyager
Another ingress based on HAProxy under the covers. Voyager is packaged up nicely and the docs look good. I couldn’t see where the load balancing algorithms were configured so assumed it’s just defaulting to round robin. If that’s wrong let me know in the comments and I’ll update.
6. Contour
Based on Envoy this has some more modern features like supporting Canary deploys. It also has a good set of load balancing algorithms and support for a variety of protocols. Unlike some of the others listed I got the impression from Github that this is under pretty rapid development still. There are discussions about adding more features which seems promising.
7. Ambassador
As mentioned above this one isn’t technically an ingress if you go by the strict Kubernetes definition. With Ambassador you simply annotate your services and it acts like an ingress by routing traffic. Ambassador has some very cool features that none of the other ingresses have like traffic shadowing which allows you to test services in a live production environment by mirroring request data.
Ambassador integrates nicely with both Opentracing and Istio.
8. Istio Ingress
If you’re already running Istio then this is probably a good default choice. It has some of the more modern features that Ambassador has. It also has fault injection which looks like it might be fun to play with. However, Istio is currently doing a lot of work in this area and is moving away from Ingress towards Gateways. So if you’re looking for something that’s not changing every 5 seconds you may want to still consider Ambassador.
Istio ingress also doesn’t support things like redirect from cleartext to TLS & authentication which are common features you want in your edge.
9. Gloo Solo
Gloo has some unique features like function based routing and service discovery across multiple IaaS, FaaS and PaaS providers. This is definitely the Ingress you should evaluate if you’re moving heavily in a serverless direction.
Summary
There’s no clear winner in this one because you’re going to need to pick the ingress based on your requirements. No single ingress currently does it all.
The safest choice is ingress-nginx. This is the one that most people use and it’s extremely reliable. The problem with ingresses is that when there’s a problem literally everyone complains. Ingress-nginx will cover 99% of use cases, so start here and then test others in a dev environment for a while before switching. Before you begin I’d recommend you read this blog to get ahead of some of the problems you may encounter.
Edit: As of 2021 I’ve switched over to Traefik and I notice quite a few other companies have done the same. It’s simple, works very well and I’ve had zero issues with it in production.
Historical workbook values; blanks mean unknown, not No. Prices, versions, maturity labels and feature claims are not current recommendations.
Kubernetes Ingress / Transposed (historical)
Historical snapshotRecovered comparison data. Versions, prices and availability describe the original research, not a current benchmark. Blank or damaged source values are marked unknown.
Choose columns
| Historical controller | backend service discovery | Protocol: all | Protocol: http | Protocol: https | Protocol: tcp | Protocol: tcp+tls | Protocol: udp | Protocol: grpc | based on | ssl termination | websocket | routing | scope | resiliency | lb algorithms | auth | Column 18 (unnamed) | Tracing | canary/shadow | istio integration | state | Paid support | link | dashboard | sticky sessions | lua |
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| ingress-nginx | dynamic | http,https,tcp (separate lb),udp,grpc,fastcgi,IPC socket | Yes | Yes | Yes | Unknown | Yes | Yes | nginx | yes | yes | host,path(with regex) | cross-namespace | rate limit, retries | rr,ewma,ip_hash | basic, digest, external auth | Unknown | yes | canary | - | kubernetes | - | https://kubernetes.github.io/ingress-nginx/ | Metrics can be seen in Grafana | Yes | Yes |
| ambassador | dynamic | http,https,grpc,tcp, tcp+ssl/tls | Yes | Yes | Yes | Yes | No | Yes | envoy | yes | yes | host,header,path | cross-namespace | circuit break, rate limit, retries | wrr,ring hash,maglev | yes | Unknown | yes | canary,shadow | yes | kubernetes | yes | https://www.getambassador.io/ | Metrics can be seen in Grafana and Prometheus | Yes | Yes(envoy) |
| gloo (solo.io) | dynamic | http, https, grpc, tcp, tcp+ssl/tls, graphql, swagger, lambdas | Yes | Yes | Yes | Yes | No | Yes | envoy | yes | yes | header, query param, http method, path, plugin, function | cross-namespace | circuit break, rate limit, retries, prometheus & grafana, role delegation, tracing, traffic shifting, shadowing | round robin, least request, ring hash, maglev, random | tls, vault secrets, custom authentication, data loss prevention, WAF, API Key, JWT, LDAP, OAuth, OIDC, OPA, Custom | Unknown | yes | canary & shadow | yes | kubernetes, nomad | yes | https://www.solo.io/products/gloo/ | Admin Dashboard + Prometheus and Grafana | Yes | Yes (envoy) |
| traefik | dynamic | http,https,grpc,tcp + tls (alpha) | Yes | Yes | Unknown | Yes | Unknown | Yes | traefik | yes | yes | host,path | cross-namespace | circuit break, retries | rr, wrr | basic, digest and forward auth in alpha | Unknown | yes | canary | - | kubernetes | yes | https://docs.traefik.io/configuration/backends/kubernetes/ | Included | Yes(traefik.ingress.kubernetes.io/affinity: "true") | No |
| kong | dynamic | http,https, grpc | Yes | Yes | Yes | Yes | No | Yes | nginx | yes | yes | host, header, path, method | cross-namespace | active and passive health check, circuit break, rate limit, retries | rr, hash, header, cookie | Basic Auth, HMAC, JWT, Key, LDAP, OAuth 2.0, PASETO, plus paid Kong Enterprise options like OpenID Connect | Unknown | yes | canary | yes | kubernetes | yes | https://github.com/Kong/kubernetes-ingress-controller | Admin Dashboard + Grafana+Prometheus statsd Datadog SignalFx | Yes | Yes(nginx) |
| istio ingress | dynamic | tcp,http,https,grpc | Yes | Yes | Unknown | Yes | Unknown | Yes | envoy | yes | yes | host,user | cross-namespace | circuit break, retries | rr,leastconn,random,passthrough | JWT | Unknown | yes | Unknown | yes | kubernetes | - | https://istio.io/docs/tasks/traffic-management/ingress/ | Metrics can be seen in Grafana and Prometheus, tracing can be seen through jaeger or zipkin UI | Yes | Yes(envoy) |
| contour | dynamic | http,https,tcp,grpc | Yes | Yes | Yes | Unknown | Unknown | Yes | envoy | yes | yes | host,path | cross namespace | retries | wrr,wlr,ring hash, maglev, random | - | Unknown | - | canary | - | kubernetes | - | https://github.com/heptio/contour | - | Yes | Yes(envoy) |
| haproxy | dynamic | http,tcp | Yes | Unknown | Yes | Unknown | Unknown | Unknown | haproxy | yes | yes | host,path | optional cross-namespace | - | rr, srr, leastconn,first,source,uri,url_param,hdr,rdp-cookie | basic | Unknown | - | - | - | kubernetes | yes | https://www.haproxy.com/blog/haproxy_ingress_controller_for_kubernetes/ | Metrics can be seen in Grafana or Datadog | Yes | Yes |
| Citrix Ingress Controller | dynamic | http,https,tcp,ssl-tcp,udp | Yes | Yes | Yes | Yes | Yes | Unknown | Citrix ADC | yes | yes | host,path | cross-namespace | health check | rr,least_conn,wrr,least_response,hash | basic | Unknown | - | canary | - | kubernetes | yes | https://github.com/citrix/citrix-k8s-ingress-controller | Metrics can be shown in Grfana https://github.com/citrix/netscaler-metrics-exporter | Yes | Yes |
| Unknown product (damaged row identity) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) |
| Unknown product (damaged row identity) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) | Unknown (ambiguous product association) |
| AWS ALB Ingress | Unknown | http, https | Yes | Yes | Unknown | Unknown | Unknown | Unknown | AWS ALB | yes | yes | Unknown | cross-namespace | rate-limit, health-check | Unknown | Unknown | Unknown | Unknown | Unknown | Unknown | Unknown | Unknown | https://github.com/kubernetes-sigs/aws-alb-ingress-controller | AWS CloudWatch | Unknown | Unknown |
| voyager | dynamic | http,https,tcp | Yes | Yes | Yes | Unknown | Unknown | Unknown | haproxy | yes | yes | host,path | cross-namespace | - | rr | basic,oauth | Unknown | - | - | - | kubernetes | yes | https://appscode.com/products/voyager/ | Built on top of HAProxy with similar dashboard options | Unknown | Unknown |
13 rows
Kubernetes Ingress / Ingresses (historical)
Historical snapshotRecovered comparison data. Versions, prices and availability describe the original research, not a current benchmark. Blank or damaged source values are marked unknown.
Choose columns
| Unknown (damaged historical cell) | ingress-nginx | istio ingress | traefik 2.0 | kong | contour | haproxy | citrix ingress controller | F5 Networks | voyager | AWS ALB Ingress | Tyk |
|---|---|---|---|---|---|---|---|---|---|---|---|
| auth | basic, digest, external auth | JWT | basic, digest and forward auth in alpha | Basic Auth, HMAC, JWT, Key, LDAP, OAuth 2.0, PASETO, plus paid Kong Enterprise options like OpenID Connect | - | basic | basic | Wide range of auth options with APM module | basic,oauth | Unknown | Basic, Token, OpenID, HMAC, OAuth 2.0, Custom, mTLS, JWT (lua, js, gRPC, go) |
| Tracing | yes | yes | yes | yes | - | - | - | - | - | Unknown | yes |
| istio integration | - | yes | - | yes | - | - | - | - | - | Unknown | - |
| linkerd2 | yes | - | yes | - | - | yes | - | - | Unknown | Unknown | - |
| canary/shadow | canary | Unknown | canary, mirroring | canary | canary | - | canary | Blue-Green Deployment, A/B Deployment | - | Unknown | With goreplay plugin https://github.com/buger/goreplay |
| scope | cross-namespace | cross-namespace | cross-namespace | cross-namespace | cross namespace | optional cross-namespace | cross-namespace | cross-namespace | cross-namespace | cross-namespace | cross-namespace |
| backend service discovery | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic |
| based on | nginx | envoy | traefik | nginx + openresty | envoy | haproxy | Citrix ADC | F5 ADC | haproxy | AWS ALB | Go - Tyk |
| routing | host,path(with regex) | host,user | host,path | host,path (with regex), method, header | host,path | host,path | host,path | - Full Ingress support - Openshift Routes - Any L3/L4/L7 info when using AS3 Extension integration | host,path | Unknown | host, path, method, header RE2 Regexp |
| protocol | http,https,tcp (separate lb),udp,grpc,fastcgi,IPC socket | tcp,http,https,grpc | http,https,grpc,tcp + tls | http,https, grpc, tcp, tcp+tls | http,https,tcp,grpc | http,tcp | http,https,tcp,ssl-tcp,udp | tcp, http, https | http,https,tcp,grpc | http, https | http, https, gRPC, TCP, TLS-TCP |
| link | https://kubernetes.github.io/ingress-nginx/ | https://istio.io/docs/tasks/traffic-management/ingress/ | https://docs.traefik.io/providers/kubernetes-crd/ | https://github.com/Kong/kubernetes-ingress-controller | https://github.com/projectcontour/contour | https://www.haproxy.com/blog/haproxy_ingress_controller_for_kubernetes/ | https://github.com/citrix/citrix-k8s-ingress-controller | https://github.com/istio/api/blob/master/networking/v1alpha3/gateway.proto | https://appscode.com/products/voyager/ | https://github.com/kubernetes-sigs/aws-alb-ingress-controller | https://github.com/TykTechnologies/tyk-helm-chart/#using-the-ingress-controller |
| state | kubernetes | kubernetes | kubernetes | kubernetes | kubernetes | kubernetes | kubernetes | kubernetes | kubernetes | Unknown | Unknown |
| dashboard | Metrics can be seen in Grafana | Metrics can be seen in Grafana and Prometheus, tracing can be seen through jaeger or zipkin UI | Included; https://docs.traefik.io/observability/metrics/prometheus/ | Grafana+Prometheus statsd Datadog SignalFx | Metrics can be seen in Grafana and Prometheus | Metrics can be seen in Grafana or Datadog | Metrics can be shown in Grfana https://github.com/citrix/netscaler-metrics-exporter | built in dashboard + export with Telemetry Services which include https://clouddocs.f5.com/products/extensions/f5-telemetry-streaming/latest/ | Built on top of HAProxy with similar dashboard options | AWS CloudWatch | Tyk Dashboard, Prometheus, StatsD, DataDog, Logz.io, Loggly, Splunk https://github.com/TykTechnologies/tyk-pump/tree/master/pumps |
| resiliency | rate limit, retries | circuit break, retries | https://docs.traefik.io/middlewares/overview/ ; CircuitBreaker, RateLimit, Retry, Buffering, many more. | active and passive health check, circuit break, rate limit, retries | retries | - | health check | active and passive health check, ramp-up, rate limit, retries | - | rate-limit, health-check | uptime tests, enforced timeouts, circuit breaker, throttling |
| lb algorithms | rr,ewma,ip_hash | rr,leastconn,random,passthrough | HTTP: rr, wrr, mirroring; TCP: RR, WRR;HTTPS | rr, hash, header, cookie | wrr,wlr,ring hash, maglev, random | rr, srr, leastconn,first,source,uri,url_param,hdr,rdp-cookie | rr,least_conn,wrr,least_response,hash | “dynamic-ratio-member”, “dynamic-ratio-node”, “fastest-app-response”, “fastest-node”, “least-connections-member”, “least-connections-node”, “least-sessions”, “observed-member”, “observed-node”, “predictive-member”, “predictive-node”, “ratio-least-connections-member”, “ratio-least-connections-node”, “ratio-member”, “ratio-node”, “ratio-session”, “round-robin”, “weighted-least-connections-member”, “weighted-least-connections-node” | rr | Unknown | rr |
| ssl termination | yes | yes | yes | yes | yes | yes | yes | yes | yes | yes | yes |
| websocket | yes | yes | yes | yes | yes | yes | yes | yes | yes | yes | yes |
| Paid support | - | - | yes | yes | yes | yes | yes | yes | yes | Unknown | yes |
| sticky sessions | Yes | Yes | Yes(traefik.ingress.kubernetes.io/affinity: "true") | Yes | Yes | Yes | Yes | - | Unknown | Unknown | Unknown |
| lua | Yes | Yes(envoy) | will | Yes(nginx) | Yes(envoy) | Yes | Yes | - | Unknown | Unknown | lua plugin support |
20 rows
Kubernetes Ingress / Copy of Ingresses (historical)
Historical snapshotRecovered comparison data. Versions, prices and availability describe the original research, not a current benchmark. Blank or damaged source values are marked unknown.
Choose columns
| Feature / source label | ingress-nginx | ambassador | traefik | kong | istio ingress | contour | haproxy | citrix ingress controller | Gloo Solo | F5 Networks | AWS ALB Ingress | voyager |
|---|---|---|---|---|---|---|---|---|---|---|---|---|
| backend service discovery | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic | dynamic |
| protocol | http,https,tcp (separate lb),udp,grpc,fastcgi,IPC socket | http,https,grpc,tcp, tcp+ssl/tls | http,https,grpc,tcp + tls (alpha) | http,https, grpc | tcp,http,https,grpc | http,https,tcp,grpc | http,tcp | http,https,tcp,ssl-tcp,udp | tcp,http,https,grpc | tcp, http, https | http, https | http,https,tcp |
| based on | nginx | envoy | traefik | kong (nginx) | envoy | envoy | haproxy | Citrix ADC | envoy | F5 ADC | AWS ALB | haproxy |
| ssl termination | yes | yes | yes | yes | yes | yes | yes | yes | yes | yes | yes | yes |
| websocket | yes | yes | yes | yes | yes | yes | yes | yes | yes | yes | yes | yes |
| routing | host,path(with regex) | host,header,path | host,path | host,path (with regex), method, header | host,user | host,path | host,path | host,path | header, query param, http method, path, plugin, function | - Full Ingress support - Openshift Routes - Any L3/L4/L7 info when using AS3 Extension integration | Unknown | host,path |
| scope | cross-namespace | cross-namespace | cross-namespace | cross-namespace | cross-namespace | cross namespace | optional cross-namespace | cross-namespace | cross-namespace | cross-namespace | cross-namespace | cross-namespace |
| resiliency | rate limit, retries | circuit break, rate limit, retries | circuit break, retries | active and passive health check, circuit break, rate limit, retries | circuit break, retries | retries | - | health check | rate limit, health check | active and passive health check, ramp-up, rate limit, retries | rate-limit, health-check | - |
| lb algorithms | rr,ewma,ip_hash | wrr,ring hash,maglev | rr, wrr | rr, hash, header, cookie | rr,leastconn,random,passthrough | wrr,wlr,ring hash, maglev, random | rr, srr, leastconn,first,source,uri,url_param,hdr,rdp-cookie | rr,least_conn,wrr,least_response,hash | rr, least request, random | “dynamic-ratio-member”, “dynamic-ratio-node”, “fastest-app-response”, “fastest-node”, “least-connections-member”, “least-connections-node”, “least-sessions”, “observed-member”, “observed-node”, “predictive-member”, “predictive-node”, “ratio-least-connections-member”, “ratio-least-connections-node”, “ratio-member”, “ratio-node”, “ratio-session”, “round-robin”, “weighted-least-connections-member”, “weighted-least-connections-node” | Unknown | rr |
| auth | basic, digest, external auth | yes | basic, digest and forward auth in alpha | Basic Auth, HMAC, JWT, Key, LDAP, OAuth 2.0, PASETO, plus paid Kong Enterprise options like OpenID Connect | JWT | - | basic | basic | basic, oidc, custom | Wide range of auth options with APM module | Unknown | basic,oauth |
| Tracing | yes | yes | yes | yes | yes | - | - | - | yes | - | Unknown | - |
| canary/shadow | canary | canary,shadow | canary | canary | Unknown | canary | - | canary | canary | Blue-Green Deployment, A/B Deployment | Unknown | - |
| istio integration | - | yes | - | - | yes | - | - | - | yes | - | Unknown | - |
| state | kubernetes | kubernetes | kubernetes | kubernetes | kubernetes | kubernetes | kubernetes | kubernetes | kubernetes | kubernetes | Unknown | kubernetes |
| Paid support | - | yes | yes | yes | - | - | yes | yes | yes | yes | Unknown | yes |
| link | https://kubernetes.github.io/ingress-nginx/ | https://www.getambassador.io/ | https://docs.traefik.io/configuration/backends/kubernetes/ | https://github.com/Kong/kubernetes-ingress-controller | https://istio.io/docs/tasks/traffic-management/ingress/ | https://github.com/heptio/contour | Unknown (damaged historical cell) | https://github.com/citrix/citrix-k8s-ingress-controller | https://gloo.solo.io/ | https://github.com/istio/api/blob/master/networking/v1alpha3/gateway.proto | https://github.com/kubernetes-sigs/aws-alb-ingress-controller | https://appscode.com/products/voyager/ |
| dashboard | Metrics can be seen in Grafana | Metrics can be seen in Grafana and Prometheus | Included | Grafana+Prometheus statsd Datadog SignalFx | Metrics can be seen in Grafana and Prometheus, tracing can be seen through jaeger or zipkin UI | - | Metrics can be seen in Grafana or Datadog | Metrics can be shown in Grfana https://github.com/citrix/netscaler-metrics-exporter | Metrics can be seen in Grafana and Prometheus | built in dashboard + export with Telemetry Services which include: Splunk Microsoft Azure Log Analytics AWS Cloud Watch AWS S3 Graphite Kafka ElasticSearch Sumo Logic StatsD Generic HTTP See more in https://clouddocs.f5.com/products/extensions/f5-telemetry-streaming/latest/ Show less | AWS CloudWatch | Built on top of HAProxy with similar dashboard options |
| sticky sessions | Yes | Yes | Yes(traefik.ingress.kubernetes.io/affinity: "true") | Yes | Yes | Yes | Yes | Yes | yes | - | Unknown | Unknown |
| lua | Yes | Yes(envoy) | No | Yes(nginx) | Yes(envoy) | Yes(envoy) | Yes | Yes | Yes(envoy) | - | Unknown | Unknown |
19 rows
Sources & further reading
Spotted something that needs another look?
Help improve this page →